Pular para o conteúdo
Informática

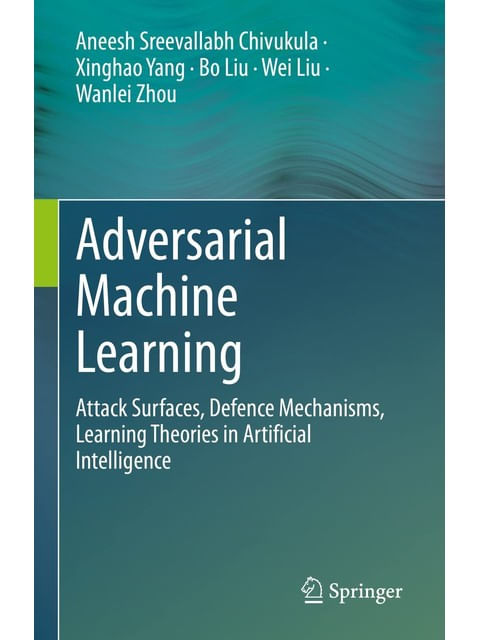
Adversarial Machine Learning

Attack Surfaces, Defence Mechanisms, Learning Theories In Artificial Intelligence

1ª Edição - 2023302 páginasSpringeren
Seja o primeiro a avaliar
Sua leitura no Lireo

Guarde este livro na sua estante

Crie uma conta gratuita e continue exatamente desta página.

Registre seu progresso de leitura
Descubra outros leitores do mesmo livro
Participe de clubes de leitura
Organize toda sua biblioteca

Sinopse

A critical challenge in deep learning is the vulnerability of deep learning networks to security attacks from intelligent cyber adversaries. Even innocuous perturbations to the training data can be used to manipulate the behaviour of deep networks in unintended ways. In this book, we review the latest developments in adversarial attack technologies in computer vision; natural language processing; and cybersecurity with regard to multidimensional, textual and image data, sequence data, and temporal data. In turn, we assess the robustness properties of deep learning networks to produce a taxonomy of adversarial examples that characterises the security of learning systems using game theoretical adversarial deep learning algorithms. The state-of-the-art in adversarial perturbation-based privacy protection mechanisms is also reviewed. We propose new adversary types for game theoretical objectives in non-stationary computational learning environments. Proper quantification of the hypothesis set in the decision problems of our research leads to various functional problems, oracular problems, sampling tasks, and optimization problems. We also address the defence mechanisms currently available for deep learning models deployed in real-world environments. The learning theories used in these defence mechanisms concern data representations, feature manipulations, misclassifications costs, sensitivity landscapes, distributional robustness, and complexity classes of the adversarial deep learning algorithms and their applications. In closing, we propose future research directions in adversarial deep learning applications for resilient learning system design and review formalized learning assumptions concerning the attack surfaces and robustness characteristics of artificial intelligence applications so as to deconstruct the contemporary adversarial deep learning designs. Given its scope, the book will be of interest to Adversarial Machine Learning practitioners and Adversarial Artificial Intelligence researchers whose work involves the design and application of Adversarial Deep Learning.

Planeje no seu ritmo

Quanto tempo leva para ler Adversarial Machine Learning?

Esta edição tem 302 páginas. Escolha uma meta diária possível e ajuste o plano conforme a leitura avançar.

Ritmo tranquilo

31 dias

10 páginas por dia

Ritmo constante

16 dias

20 páginas por dia

Ritmo intenso

11 dias

30 páginas por dia

Detalhes do livro

Título
Adversarial Machine Learning
Autor
Aneesh Screevallabh | Yang Xinghao | Liu Bo | Liu Wei | Zhou Wanlei Chivukula
Editora
Springer
Ano
2023
Páginas
302 páginas
Idioma
EN
ISBN-13
9783030997717
Edição
1ª Edição - 2023
Formato
Hardcover

Informática

Livros na mesma categoria

Sua vida de leitura

A leitura de Adversarial Machine Learning pode continuar na Lireo

A Lireo é uma plataforma para organizar sua estante, registrar páginas e impressões, publicar resenhas e encontrar pessoas que estão lendo os mesmos livros.

Blog Lireo

Dicas e recomendações para leitores

Soluções institucionais

Para escolas, universidades, autores e editoras